 ShizuStore
Monica
1.0.328-26111712-04 · GitHub
More about this app
Local-first Bitwarden/KeePass password vault with TOTP; Shizuku keeps autofill protection running in the background.
Monica 本地密码库
中文 | English | 日本語 | Tiếng Việt | Русский | 黑羽川

聚合 Bitwarden 与 KeePass 的本地优先密码库
Android · Local Vault · TOTP · WebDAV Backup

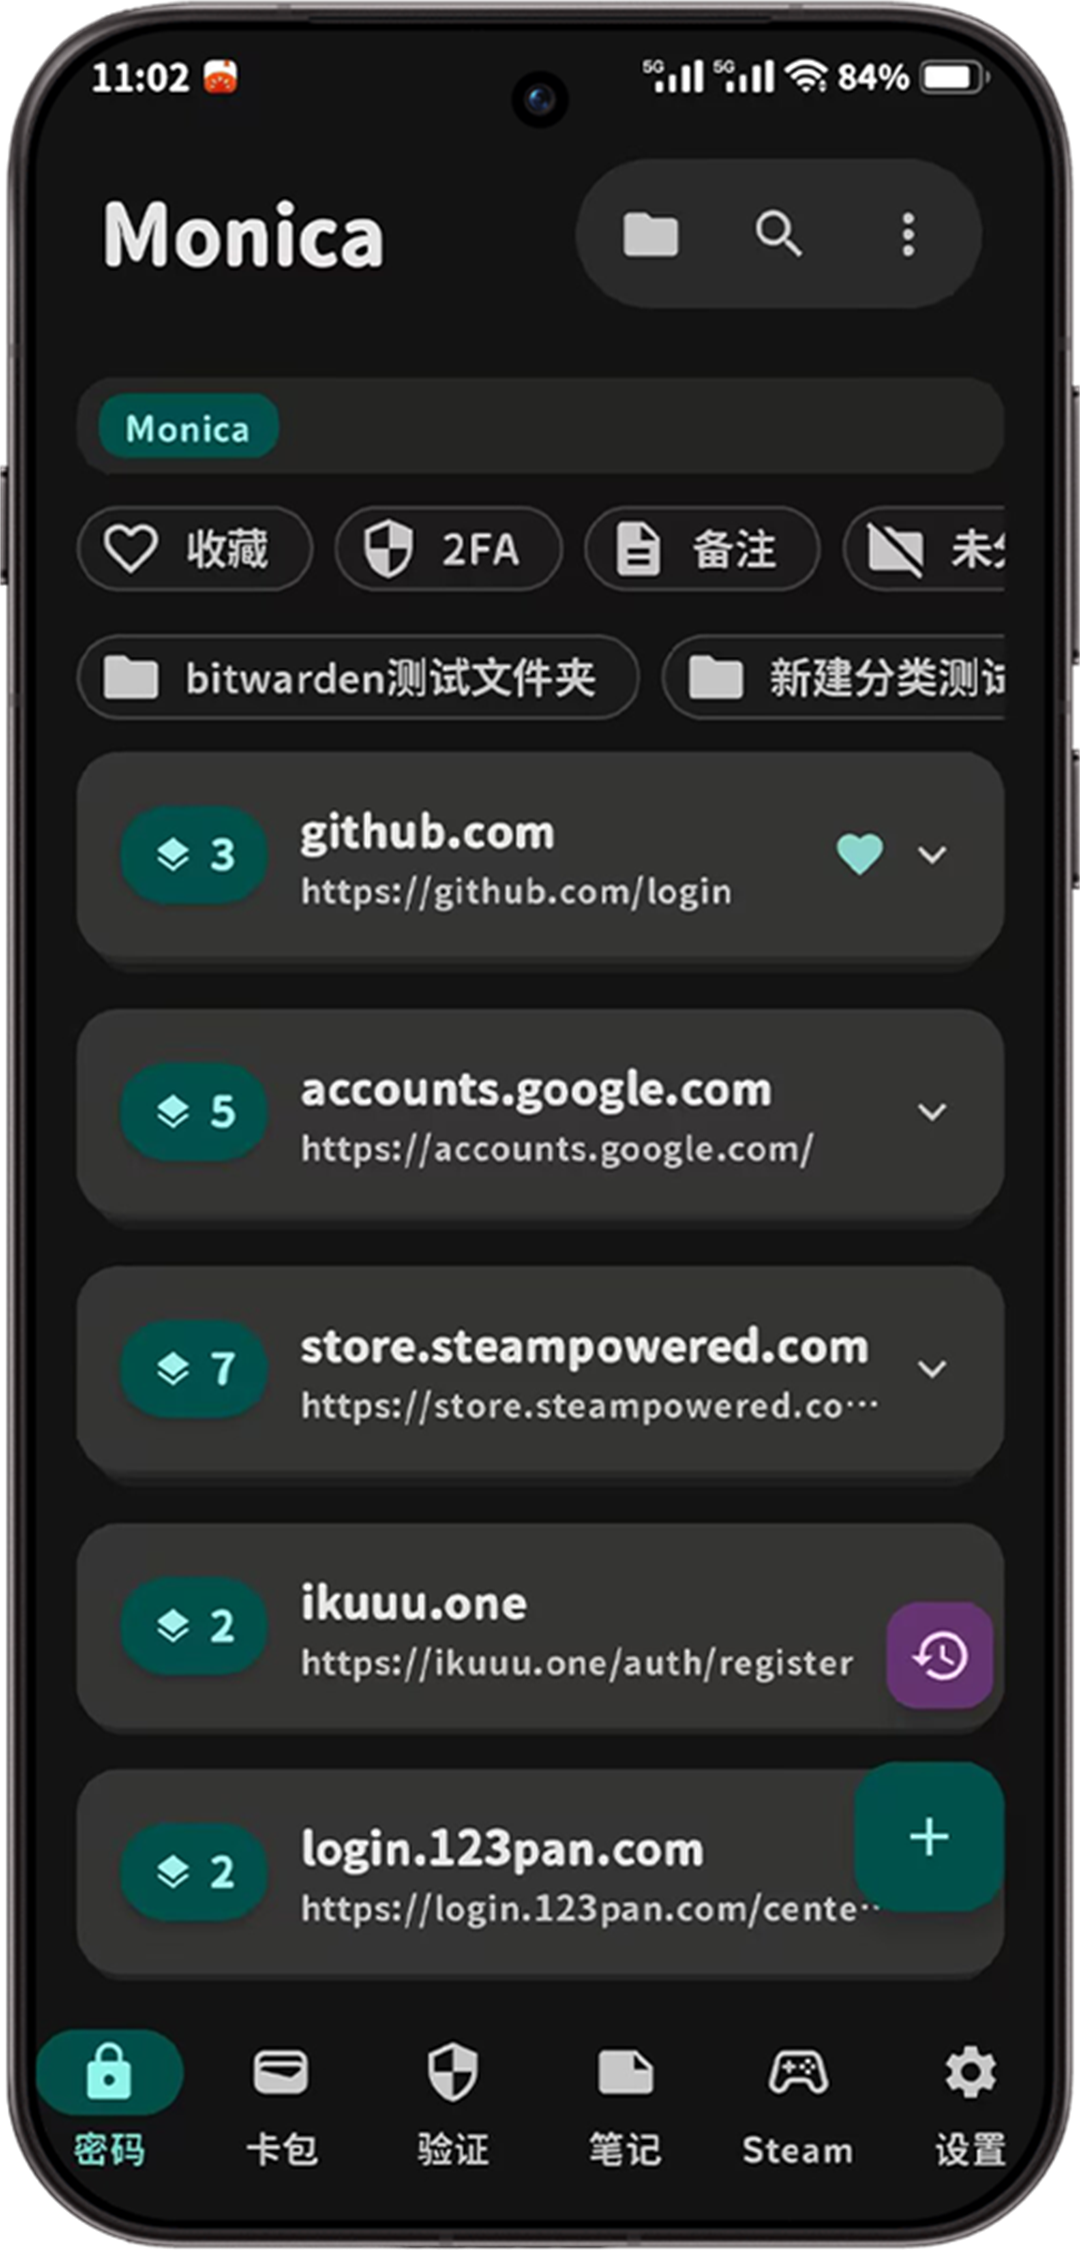
Monica 是一个聚合 Bitwarden 与 KeePass 的本地密码库(Local Vault)。 它以本地存储优先为核心,帮助你在 Android 设备上统一管理账号密码、2FA、私密笔记与敏感附件。
官网入口: https://monica-pass.github.io/MonicaDocs/
用户先看
Monica 适合谁
- 需要本地优先密码管理,不希望账号数据托管到第三方云。
- 既使用 Bitwarden,也维护 KeePass (
.kdbx) 数据。 - 需要在 Android 应用和手机浏览器中使用自动填充。
你能得到什么
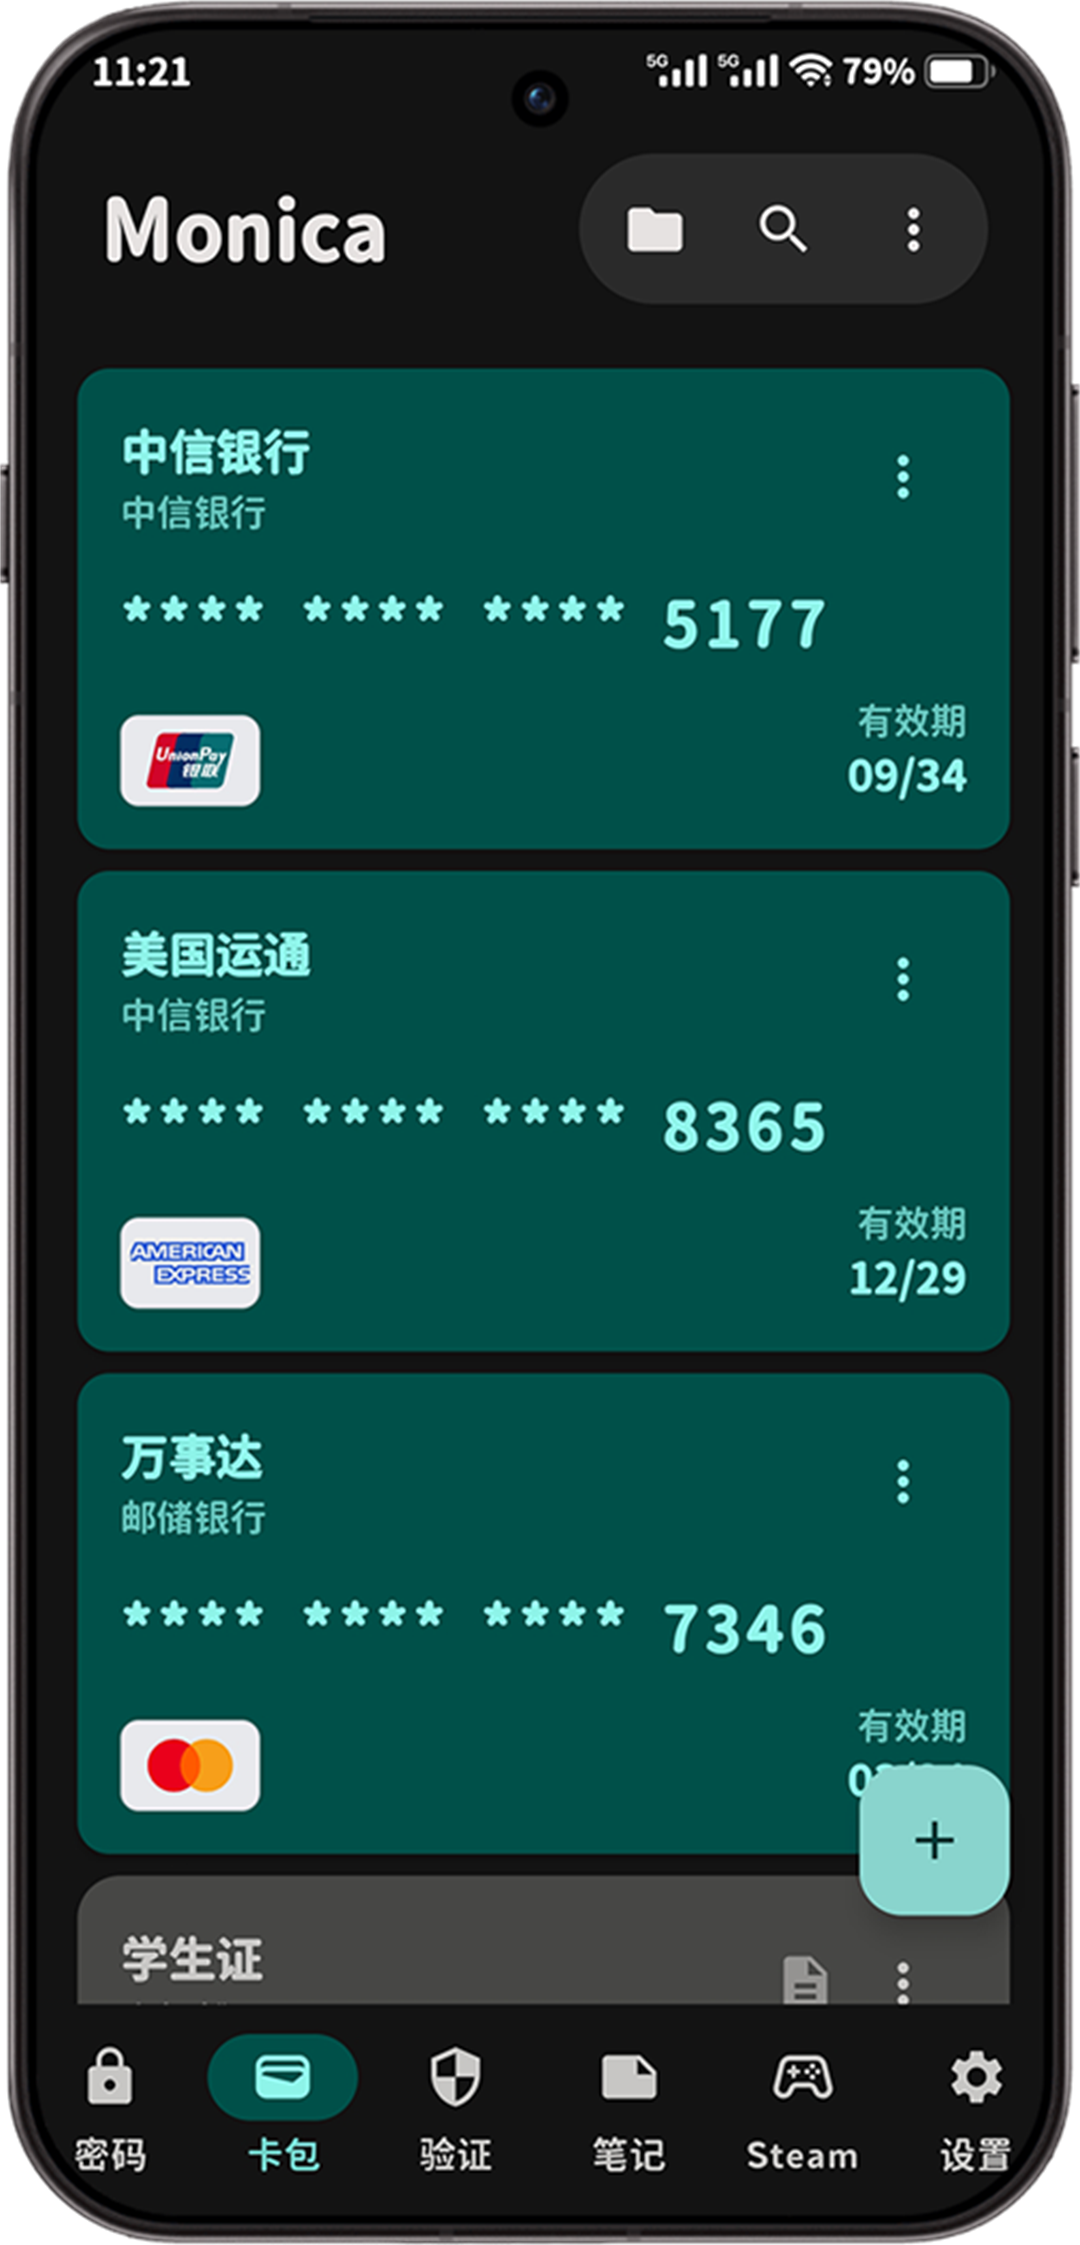
- 本地加密保险箱: 登录信息、银行卡、身份信息、私密笔记、附件。
- 双生态聚合: Android 端包含 Bitwarden API/同步能力与 KeePass (
.kdbx) 读写能力。 - 可选同步与备份: WebDAV 备份及远端库同步、OneDrive 备份与文件访问,以及配对后的局域网传输。
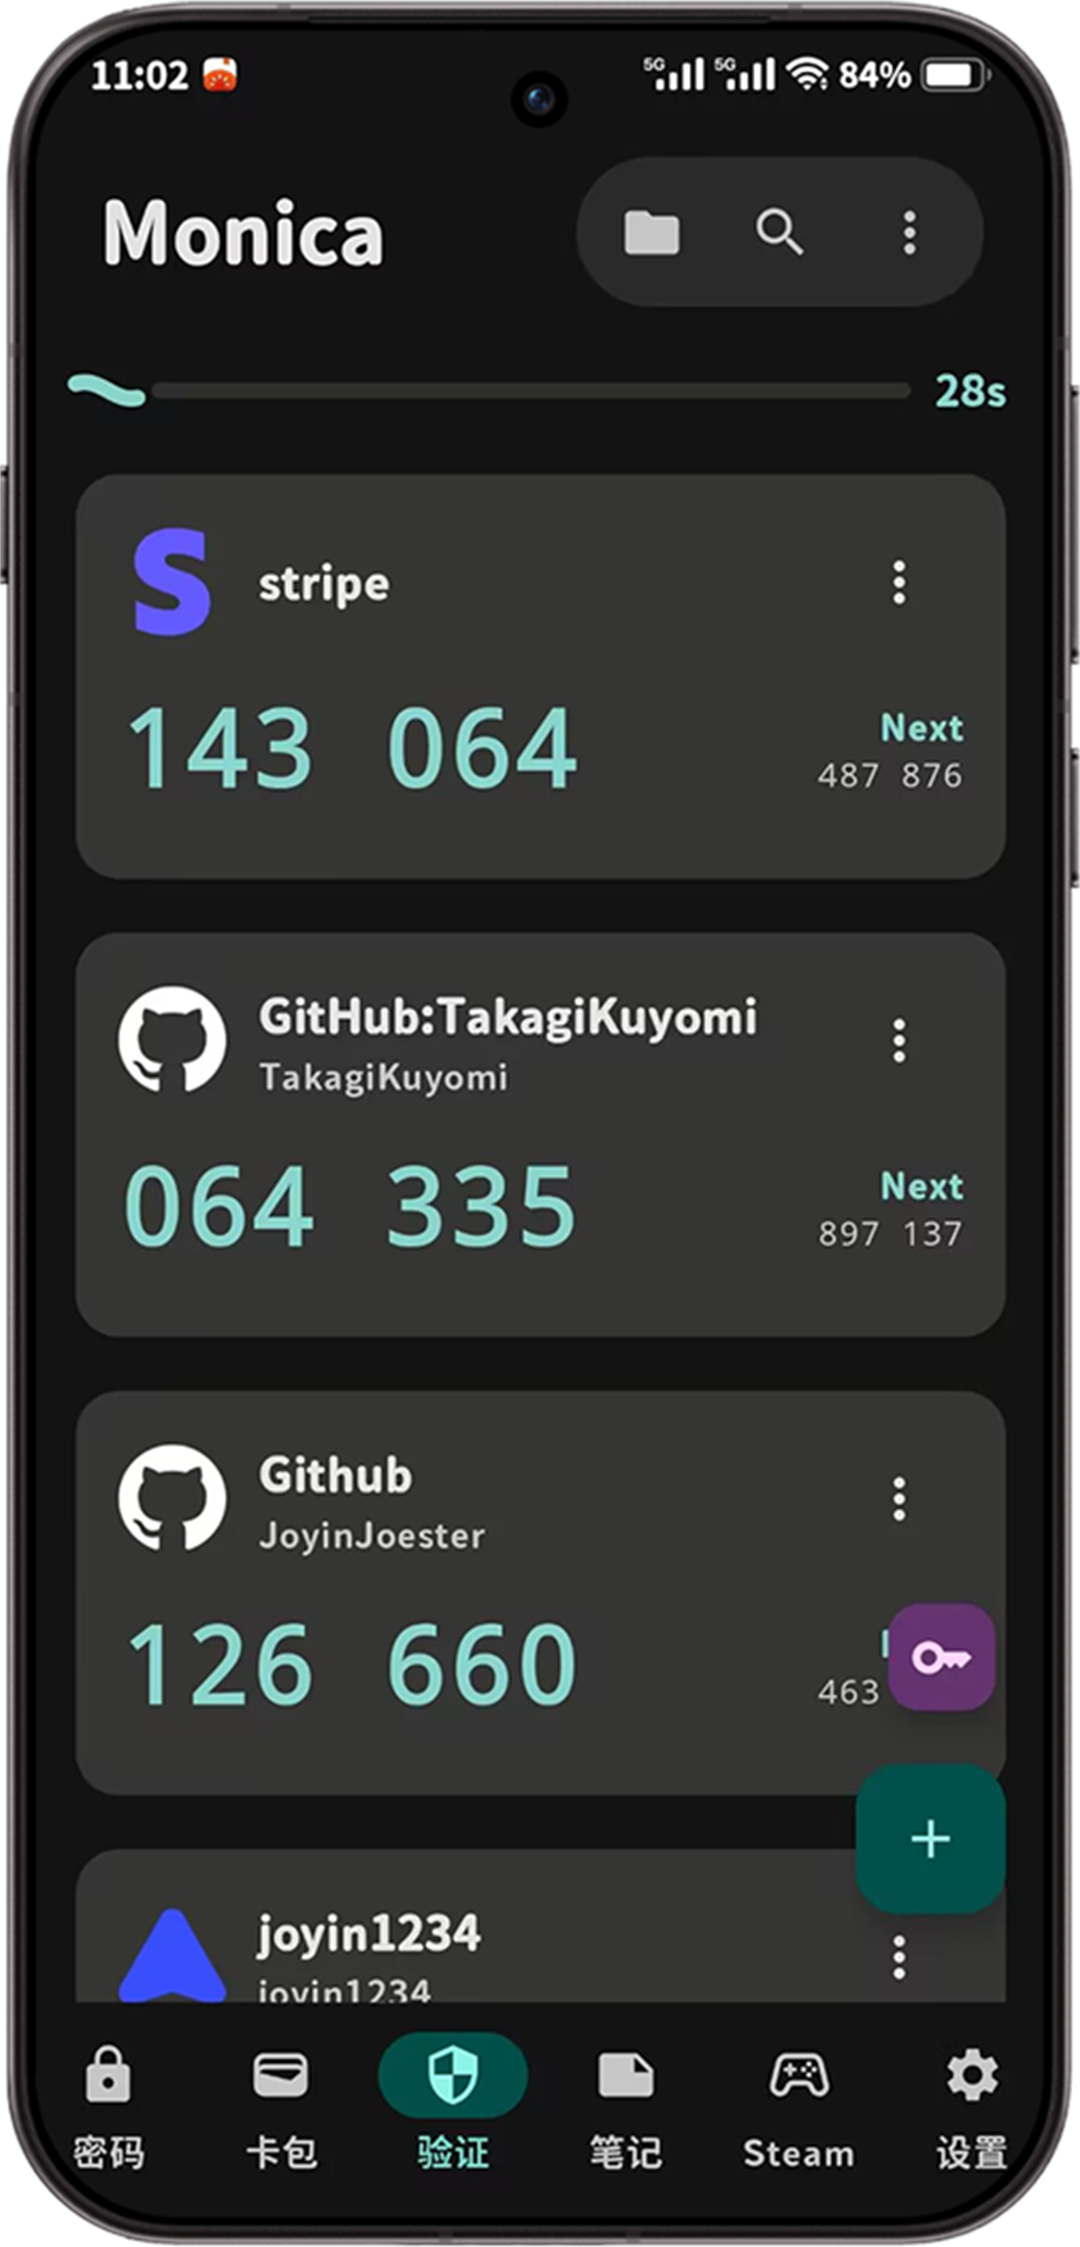
- 内置 TOTP: 在同一应用内完成密码与二次验证码管理。
MDBX 本地数据库格式
跨端开发与 AI 适配请先遵守 Monica MDBX 存储兼容契约,其中区分了核心格式、业务类型、未知字段保留和同步验收要求。 MDBX 是 Monica 正在推进的本地优先加密 vault 格式。它不是简单的密码表,而是围绕嵌套文件夹、附件、提交历史、冲突检测、tombstone 删除链路、快照恢复和 Tiga 安全模式设计的数据库格式。
如果你要在其他客户端接入 MDBX,请先读 MDBX workspace 说明 和 MDBX 客户端接入指南。完整格式规范在 mdbx/docs。
快速安装
- 从 Releases 下载最新 APK。
- 在 Android 8.0+ 设备安装并初始化主密码。
已知限制
- 由于系统兼容性原因,Monica for Android 目前在部分小米 HyperOS 设备上无法创建通行密钥(Passkey)。可以尝试酷 U 提供的解决模块:HyperMonica。
Android 版本重点
核心功能
- 本地 Vault: 所有核心凭据本地加密存储。
- 聚合导入: 支持 KeePass 数据迁移与 Bitwarden 兼容接入。
- 智能检索: 按标题、域名、标签快速定位凭据。
- 生物识别解锁: 使用系统级生物识别能力提升安全与可用性。
- TOTP 管理: 统一存储并生成动态验证码。
实现说明
- UI 层: Jetpack Compose + Material 3 Expressive + Navigation Compose。
- 数据层: Room(
PasswordDatabase)+ DAO + Repository,并接入原生 KDBX 与 MDBX 存储。 - 并发模型: Kotlin Coroutines + Flow。
- 依赖装配: 通过构造函数、工厂及应用入口显式传递依赖。
- 安全能力: Android Keystore、EncryptedSharedPreferences、BiometricPrompt。
- 同步任务: WorkManager(
AutoBackupWorker)用于自动 WebDAV 备份。 - 协议与集成: Retrofit + OkHttp(Bitwarden API)、kotpass(KeePass)、sardine-android(WebDAV)。
安全模型
- 本地敏感字段: 由
SecurityManager使用 AES-256-GCM 认证加密。 - 本地主密码校验及 MDK 密码包装密钥:PBKDF2-HMAC-SHA256,1.0.327 新写入使用 600,000 次迭代。历史 100,000 次 PBKDF2 和 Argon2id 数据保留兼容,成功验证原密码后迁移,保留原 MDK 与记录密文。
- 便携加密备份:兼容 V1 使用 PBKDF2-HMAC-SHA256/100,000 次,增强 V2 使用 600,000 次;备份格式与本地主密码保护分别处理。
- 主密码找回:安全问题答案加本次系统锁屏凭据确认(Android 11+),一次性授权在取消、后台或锁定时撤销。新答案采用随机盐与 600,000 次 PBKDF2-HMAC-SHA256,旧 SHA-256 答案和备份保留兼容;尝试次数跨页面和进程重启保留。
- Bitwarden、KeePass 与 MDBX: 使用各自格式和配置规定的加密及密钥派生方式。
- 本地保护: 主密码哈希与安全配置由本地安全组件管理。
- 网络边界: 应用声明网络权限,用于 Bitwarden、WebDAV、OneDrive、局域网传输和更新检查等功能。
赞助支持
如果 Monica 对你有帮助,欢迎支持持续开发与安全投入。

微信 / 支付宝扫码支持
你的支持将优先用于:
- 安全审计与加密方案强化。
- Android 体验优化与稳定性改进。
- 跨端功能统一与文档维护。
爱发电鸣谢
感谢每一位支持 Monica 的朋友!
本月打赏金额:¥10.00
 1503384107 ¥180.00 |  半夏微凉 ¥50.00 |  名字太长会有傻子跟着念吗 ¥40.00 | 一生 ¥30.00 |  LINGYU ¥20.00 |  洛初 ¥15.00 |
toG ¥10.00 |  Memory15 ¥10.00 |  爱发电用户_70c34 ¥10.00 |  NovaX ¥10.00 | 爱发电用户_rywF ¥10.00 |  御坂07833号 ¥10.00 |
 PVPWHGAME ¥10.00 | 爱发电用户_ff493 ¥10.00 | 爱发电用户_a991e ¥10.00 | 爱发电用户_U9rq ¥10.00 | 不二 ¥10.00 | 爱发电用户_edaa4 ¥10.00 |
 爱发电用户_VYtU ¥6.66 | 爱发电用户_e928c ¥6.00 |  Vertin! ¥5.00 | 爱发电用户_ea390 ¥5.00 |  Hin ¥5.00 | 爱发电用户_f85f8 ¥5.00 |
 Alans1gn ¥5.00 |  Eamon ¥5.00 | 哇哦 ¥5.00 | 爱发电用户_xj7t ¥5.00 |  Kiana Kaslana ¥5.00 |  海之南 ¥5.00 |
 重逢海风 ¥5.00 |  yagaojun ¥5.00 | 可恶 ¥5.00 | 爱发电用户_97324 ¥5.00 |  Jursin ¥5.00 |  Memories white ¥5.00 |
爱发电用户_hAKP ¥5.00 | 森王 ¥5.00 | 爱发电用户_43357 ¥5.00 | 坏名字qwq ¥5.00 | Draking ¥5.00 |  lingtsuki ¥5.00 |
 airem ¥5.00 |  Janson ¥5.00 | 爱发电用户_0e739 ¥5.00 |
开发者信息
项目分层(代码现状)
takagi/ru/monica/ui: Compose 页面与组件。takagi/ru/monica/data: Room 实体、DAO、数据库迁移。takagi/ru/monica/repository: 数据访问封装。takagi/ru/monica/security: 加密、密钥与鉴权相关实现。takagi/ru/monica/bitwarden: API、加密、映射、同步与视图模型。takagi/ru/monica/autofill_ng: 自动填充服务与流程。takagi/ru/monica/passkey: Android 14+ Credential Provider 相关实现。takagi/ru/monica/workers: 后台任务(如自动 WebDAV 备份)。mdbx: Monica MDBX 本地数据库格式的 Rust workspace 与客户端接入文档。
主要组件(源码可验证)
- Android UI: Jetpack Compose, Material 3 Expressive, Navigation Compose。
- 数据与状态: Room, DataStore Preferences, ViewModel。
- 安全: Android Keystore, EncryptedSharedPreferences, BiometricPrompt。
- 网络与协议: Retrofit, OkHttp, Kotlinx Serialization。
- 同步与生态: sardine-android(WebDAV), kotpass(KeePass), Bitwarden API 对接。
- 异步与任务: Coroutines, Flow, WorkManager。
- 其他能力: CameraX + ZXing(二维码扫描), Credentials API(Passkey)。
构建与贡献
下表对应当前开发源码,不代表这些版本已包含在最新发布的 APK 中。
| 组件 | 当前源码配置 |
|---|---|
| 构建 JDK / Java 与 Kotlin 字节码 | JDK 17 / target 11 |
| Android SDK | compile 37 · target 34 · minimum 26(Android 8.0) |
| Gradle Wrapper / Android Gradle Plugin | 9.7.0 / 9.3.1 |
| Kotlin / KSP | 2.4.21 / 2.3.13 |
| Compose BOM | 2026.09.00 |
| Material 3 Expressive | 1.5.0-rc01,独立固定,不随 BOM |
| Room / Navigation Compose | 2.8.5 / 2.10.2 |
| Lifecycle Runtime 与 ViewModel | 2.11.0 |
| DataStore / WorkManager / CameraX | 1.3.0 / 2.12.0 / 1.6.2 |
使用与当前 AGP 兼容的 Android Studio,或直接运行 Gradle Wrapper。构建前准备 SDK Platform 37、Android NDK、Rust 和 cargo-ndk;JNI 库会从源码构建。
版本以依赖目录、Gradle Wrapper和应用构建配置为准。完整环境准备见 Android 构建说明。
cd "Monica for Android"
./gradlew :app:assembleDebug
./gradlew :app:testDebugUnitTest
# 为 x86_64 模拟器准备主包与设备测试包:
./gradlew :app:assembleDebug :app:assembleDebugAndroidTest -PincludeX86TestAbi
从仓库根目录进入 Android 工程后执行 Gradle 命令;Windows PowerShell 使用 ./gradlew.bat。默认 APK 面向 ARM;最后一条增加 x86_64 并打包测试 APK,不会自动运行设备测试。
欢迎通过 Issue / PR 参与功能和安全改进。
致谢
Monica 的设计、兼容性适配与部分功能方向,受到了以下优秀开源项目和软件的启发与帮助:
- AtomGit - 在国内托管 Monica,帮助中国大陆用户更快访问项目。
- Keyguard - Android 端密码管理器的交互设计与体验参考。
- PixelPlayer - Android 端密码库滚动条样式参考。
- Bitwarden - 开源密码管理生态、Vault 模型与同步能力的重要参考。
- KeePass - 本地密码库理念与
.kdbx生态兼容的重要基础。 - Stratum Auth - 身份验证器体验、图标资源与相关兼容支持参考。
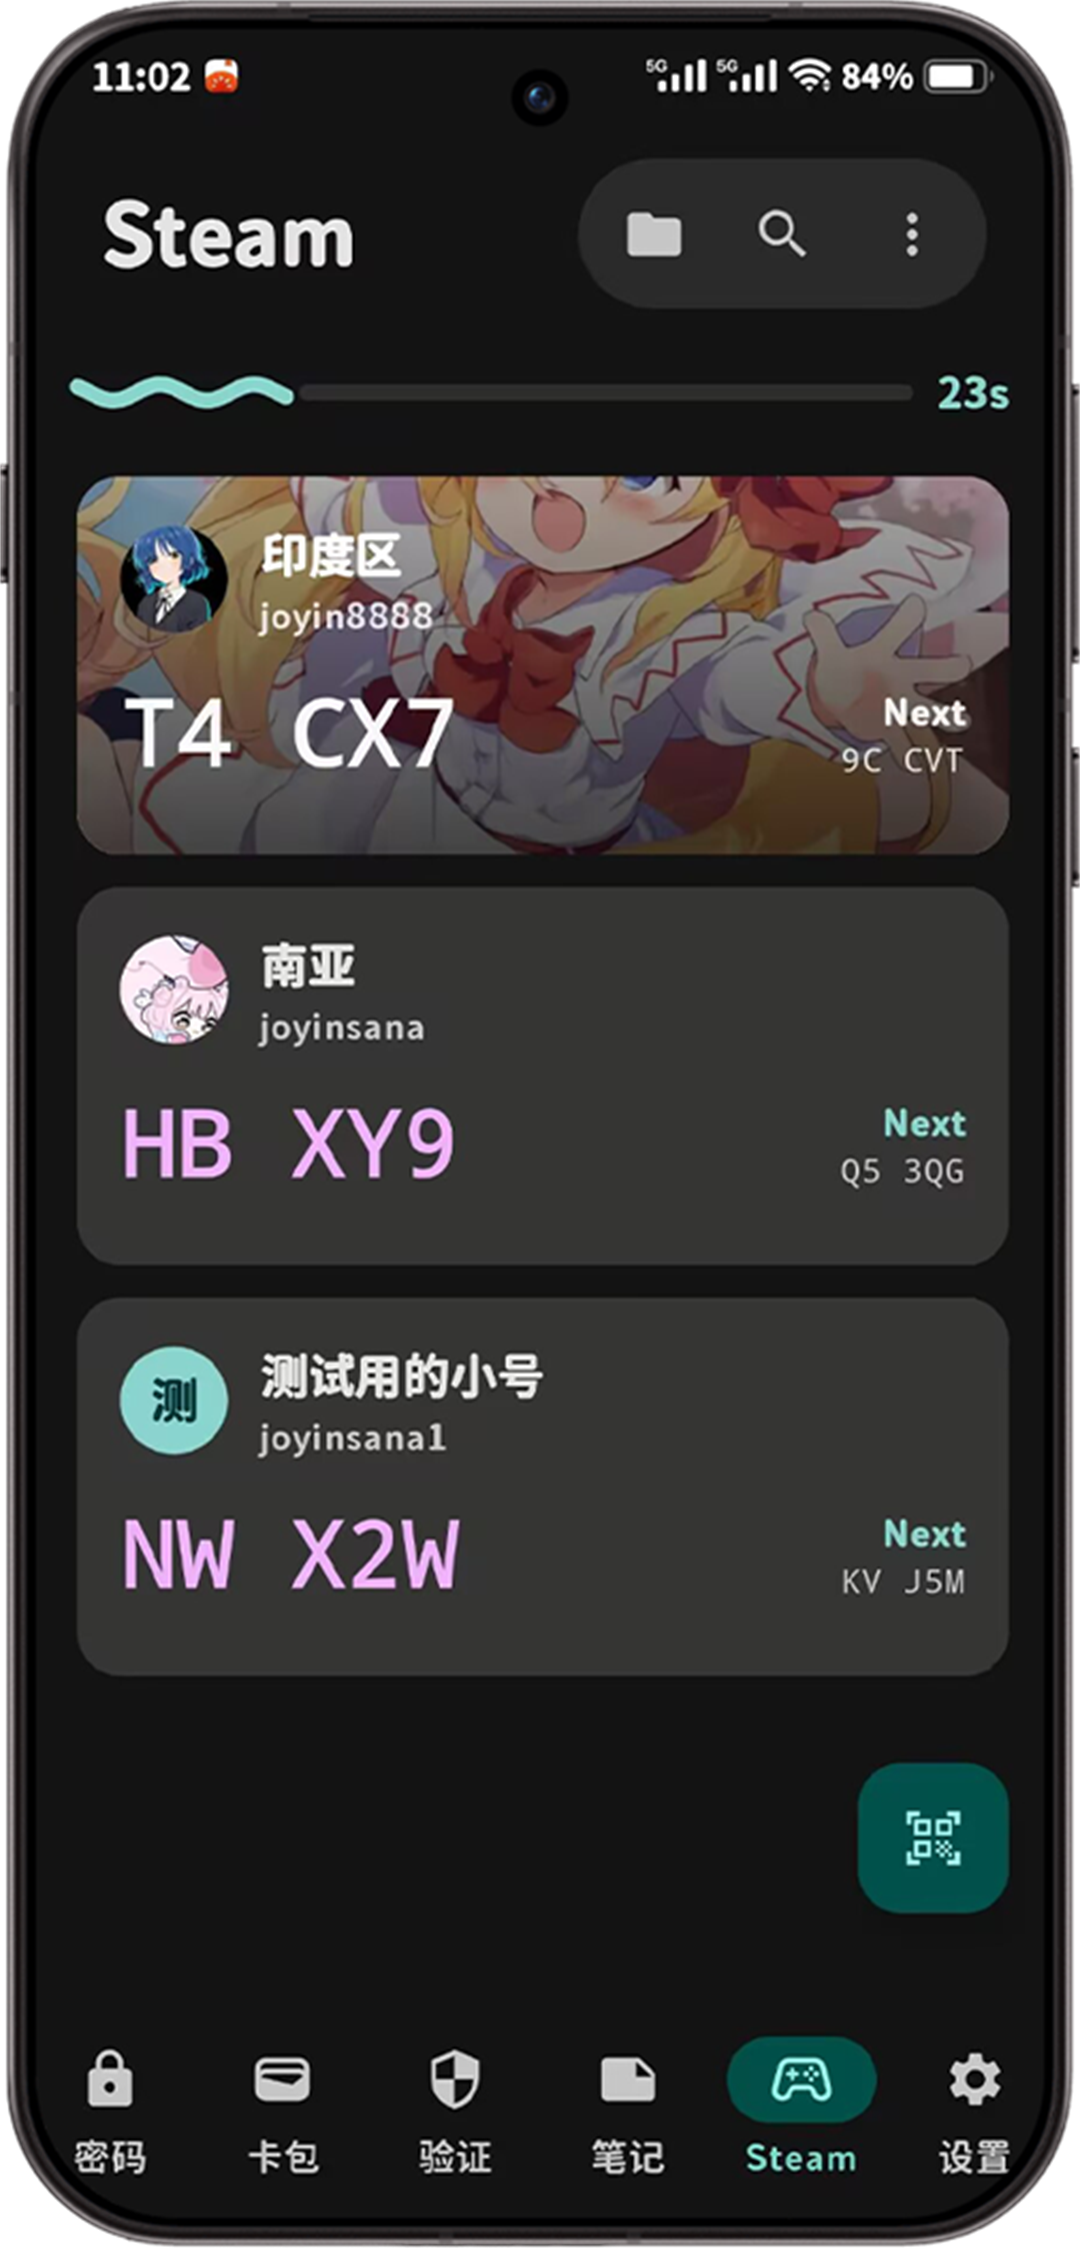
- Steam Desktop Authenticator - Steam maFile 格式、Steam Guard 与交易确认兼容性的参考。
- steamguard-cli - Steam Guard 登录、令牌迁移与确认协议实现的参考。
- AnotherVaporAuth - Steam 移动验证器、登录批准与确认流程体验的参考。
友情链接
Star History
贡献者

社区与支持
- Telegram 群组:加入 Monica 社区
许可证
Copyright (c) 2025 JoyinJoester
Monica 基于 GNU General Public License v3.0 开源发布。
第三方图标标注
- 本项目本地打包了来自 Stratum Auth app 的图标资源(版本 v1.4.0,目录 icons / extraicons,GPL-3.0)。
- 银行卡/支付卡图标来源:SVG Credit Card & Payment Icons(Apache-2.0)。
- 品牌名称与 Logo 的商标权归各自权利人所有。
F-Droid contact
For F-Droid metadata or packaging issues, contact: [email protected]
HyperOS 参考项目与致谢
感谢以下开源项目对 Monica 的 HyperOS 兼容适配提供帮助:
- Howard20181/HyperPasskey(GPL-3.0):内置可选模块的部分 Hook 实现来源,包括安全中心配置重置拦截、系统设置页、凭据选择界面及跨设备兼容。
- dingwen07/CredentialProviderManager(GPL-3.0):凭据提供方、自动填充服务及系统配置诊断的设计参考。
- cr-zhichen/password-manager-switch(MIT):默认密码管理器配置工具的系统设置读写、校验与恢复逻辑来源。
具体参考版本与适配范围见HyperOS 来源说明;随包保留 HyperPasskey GPL-3.0 许可证及 password-manager-switch MIT 声明。1.0.328 的内置模块为实验功能,默认关闭,需要兼容的模块框架,尚未经过 HyperOS 实体机验证。
Shizuku default password manager / 默认密码管理器
The Android 14+ helper in developer and autofill settings adapts the secure-settings transaction logic from cr-zhichen/password-manager-switch (MIT, copyright 2026 cr-zhichen). It targets the installed Monica edition for the current Android user, verifies writes, and supports restoring the previous configuration. The original MIT notice is included in MIT notice.
开发者设置与自动填充设置中的 Shizuku 入口参考上述原项目(MIT),用于 HyperOS 隐藏第三方密码管理器设置入口的情况。仅设置当前 Monica 版本,不导入原项目的自更新等功能;系统设置读回成功不代表所有 HyperOS 通行密钥流程均已验证。
On multi-user devices, Shizuku may also require Monica to be installed for the owner user before starting the helper for a secondary user. Only the calling user settings are changed. 多用户设备上,Shizuku 可能需要主用户也安装 Monica 才能启动副用户的辅助服务;实际更改仍限定于调用用户。
How Shizuku is used
Can restart its autofill accessibility service and set itself as default password manager via `settings` commands through Shizuku.
This is an AI-assisted analysis of Shizuku-related usages in the app's public source code. It is best effort, so it may not catch every single usage.
How this app uses Shizuku
Shizuku is used for two autofill related privileged operations with fixed system settings and no free form shell access.
- Restart accessibility autofill: the user can trigger a recovery from the autofill protection screen when the service is disconnected, and the background protection service can trigger the same recovery automatically, applied with the
settings getandsettings putshell commands through Shizuku. - Set default password manager: the user can make Monica the system credential and autofill provider from the default manager sheet, including reading the current selection, applying Monica and restoring the previous selection, applied with the
settings get,settings putandsettings deleteshell commands through Shizuku.
Android APIs or commands used
/system/bin/settings get secure enabled_accessibility_services/system/bin/settings put secure enabled_accessibility_services/system/bin/settings get secure credential_service/system/bin/settings put secure credential_service/system/bin/settings delete secure credential_service/system/bin/settings get secure credential_service_primary/system/bin/settings put secure credential_service_primary/system/bin/settings delete secure credential_service_primary/system/bin/settings get secure autofill_service/system/bin/settings put secure autofill_service/system/bin/settings delete secure autofill_service
Notable details
The accessibility recovery only restarts Monica's own service if it was already enabled, it cannot grant accessibility access and does nothing when the service was never enabled or was turned off. The default manager feature only supports Monica's own credential and autofill services on Android 14 and later, and it keeps a backup of the previous selection so the user can restore it.
Changelog
What's new for version 1.0.328-26111712-04
Monica Android 1.0.328
中文
普通密码编辑与新建现在直接提交到 MDBX 原生引擎,保留对象身份、未知字段与附件;账号组修改和删除使用同一次原生提交,继续保留历史、撤销、快照与增量同步。旧表单遇到外部修订会拒绝覆盖,保存后回读失败可安全重试;锁定或离开前台撤销编辑会话。
优化自动填充切换 KDBX、MDBX 密码库后的列表加载,减少逐条记录重复读取加密配置和查询系统状态;保留取消、锁定、发布前授权及填写时的原生修订校验。
修复密码编辑页尚未完成读取时保存可能新增同名条目的问题;完整载入原记录及关联内容后才允许保存,来源缺失或读取失败时保留原数据。
HyperOS 兼容页新增配置诊断和修复后变化检测:区分服务声明、框架识别、三项系统配置与未知状态;仅在诊断页可见或重新打开时读取比较,不自动回写,沿用 Shizuku/root 授权、审阅和恢复流程。
内置默认关闭的实验性 HyperOS 模块,分别控制安全中心配置重置拦截、系统选择页、Google 凭据选择界面及跨设备兼容;需要兼容的 LSPosed API 102+,首版限 Android 14–16 的 Xiaomi/Redmi/POCO 主用户,Google 路径需有效系统组件。未识别的方法保留原行为,框架连接不代表 Hook 已生效。
HyperOS 适配来源与致谢:Howard20181/HyperPasskey(GPL-3.0,部分内置 Hook 实现)、dingwen07/CredentialProviderManager(GPL-3.0,配置诊断设计参考)及 cr-zhichen/password-manager-switch(MIT,默认密码管理器配置逻辑)。
尚未经过 HyperOS 实体机验证。欢迎 HyperOS 用户通过 GitHub issue 反馈 ROM 版本、使用的框架及复现步骤,请勿提供密码、私钥或完整密码库。
修复部分 Steam maFile 密钥含
/时验证码显示与复制不一致的问题,完整保留密钥字符,保持原有导入和令牌权限。修复导入 KDBX 后中文或含特殊字符的分组出现同名重复文件夹、数量与进入后内容不一致的问题;统一原生分组身份,保留合法同名组和原文件。
开发者设置新增 HyperOS 兼容入口,集中现有默认密码管理器工具、HyperOS1 保存浮窗兼容和应用内减少动画选项;沿用原有授权、确认与恢复流程。
自动填充选择器按所选 Bitwarden 账号或 KDBX 数据库准备凭据,避免读取无关的 KDBX 库。
自动填充新增直接读取 MDBX 原生登录及受支持的银行卡、证件和地址,并在填写前核验当前修订;原生记录不可读、类型未知或已归档时,不回退到本地镜像。
MDBX 自动填充暂不支持绑定新网址;独立密码键盘尚未接入本轮原生 MDBX 读取。
优化自动填充选择器的本地来源加载:先恢复来源筛选,再准备所需密码和钱包内容,不再等待无关原生 KeePass 库;批量准备减少重复的有效性校验。
新增编辑器仅在打开对应页面时初始化,减少进入自动填充选择器时的额外准备。
修正选择器中新密码保存后的填充与返回衔接;切换来源、取消或锁定后,旧请求结果不再覆盖当前列表。
自动填充与输入法解锁在等待设置时保持界面响应;返回、后台或锁定后不再接收旧请求的迟到设置。
Passkey 认证初次读取所选凭据时保持界面响应;取消、进入后台或锁定后丢弃迟到的读取结果。
物理密钥页面背景延伸至状态栏,标题和关闭按钮保留安全间距,避免被系统图标遮挡。
减少笔记列表搜索与界面更新时重复建立的分类和密码库信息订阅,保留内容更新与锁定行为。
Bitwarden 自托管连接支持复用 Android 设置中安装的用户 CA;同一可信 CA 签发的有效续期证书无需重新导入,仍可使用已有的账号专用 PEM 和 mTLS 配置。
Bitwarden 官方域名仅使用系统 CA;自托管的额外信任不传递到官方域名、外部附件下载或其他网络功能,保留域名与证书有效性校验。
修复“管理原始信息”中本地多层文件夹被平铺显示的问题,可逐层进入并返回上级;新建、重命名和移动正确保留子目录关系。
English
Ordinary password creation and editing now commit directly through the native MDBX engine, preserving object identity, unknown fields and attachments. Credential-group edits and removals share one native commit with history, revert, snapshots and incremental sync retained. Stale forms reject intervening revisions, failed post-commit reads can be retried safely, and locking or leaving the foreground revokes the editor session.
Faster autofill list loading when switching KDBX or MDBX vaults by removing repeated per-record secure-settings and system checks. Cancellation, locking, authorization before publication and native revision checks when filling remain enforced.
Fixed duplicate entries when saving a password before the editor finished loading. Saving now waits for the original record and related content; missing sources or failed reads leave existing data intact.
HyperOS compatibility adds configuration diagnostics and post-repair change detection, distinguishing service declarations, framework recognition, three secure settings and unknown states. Checks run only while the diagnostics page is visible or reopened; they never rewrite settings automatically and retain the Shizuku/root authorization, review and restore flows.
Added an experimental, default-off HyperOS module with separate controls for Security Center reset interception, system selection pages, the Google credential chooser and cross-device compatibility. Requires compatible LSPosed API 102+; initially limited to Android 14–16 Xiaomi/Redmi/POCO owner users, with valid system components required for Google routes. Unrecognized methods retain original behavior; framework connection does not prove hooks work.
HyperOS references and acknowledgments: Howard20181/HyperPasskey (GPL-3.0, parts of the built-in hooks), dingwen07/CredentialProviderManager (GPL-3.0, configuration diagnostics design), and cr-zhichen/password-manager-switch (MIT, default password manager configuration logic).
Not tested on physical HyperOS devices. HyperOS users are welcome to submit a GitHub issue with their ROM version, framework and reproduction steps; do not include passwords, private keys or complete vaults.
Fixed Steam code display/copy mismatches for maFile keys containing
/; preserve the full key and existing import and token permissions.Fixed duplicate folders and count/navigation mismatches after importing KDBX groups with non-ASCII or special-character names. Native group identities remain distinct, preserving legitimate same-named groups and the original file.
Developer settings now groups HyperOS compatibility options: the existing default password manager tool, HyperOS1 save overlay workaround and reduced in-app animations, preserving their authorization, review and restore flows.
The autofill picker prepares credentials for the selected Bitwarden account or KDBX database, avoiding unrelated KDBX vault reads.
Autofill now reads native MDBX logins and supported cards, documents and addresses directly, checking their current revision before filling. Unreadable, unknown-type or archived native records never fall back to local mirrors.
MDBX autofill does not yet support binding new URLs; the separate password keyboard is outside this round of native MDBX integration.
Improved Local loading in the autofill picker: restore the source filter before preparing the required passwords and wallet items, skip unrelated native KeePass vaults, and reduce repeated validity checks through batch preparation.
Initialize each add-item editor only when its page opens, reducing work when entering the autofill picker.
Fixed the handoff from saving a new password to autofill and returning to the list; stale requests cannot replace the current list after source changes, cancellation or locking.
Autofill and keyboard unlock stay responsive while settings load; cancelled, backgrounded or locked requests reject late settings.
Passkey authentication stays responsive during the initial selected-credential lookup and discards late results after cancellation, backgrounding or locking.
The hardware security key page now draws behind the status bar while keeping its title and close button clear of system icons.
Reduced repeated category and vault subscriptions during note searches and UI updates, while preserving content updates and locking behavior.
Bitwarden self-hosted connections can reuse user CAs installed in Android settings. Valid certificate renewals under the same trusted CA need no reimport; existing account-specific PEM and mTLS settings remain available.
Official Bitwarden domains use system CAs only. Extra self-hosted trust does not extend to official hosts, foreign attachment downloads or other network features; hostname and certificate validity checks remain enforced.
Fixed flattened local folder paths in Manage original information. Browse folders level by level, return to parents, and preserve descendant paths when creating, renaming or moving local folders.
Permissions
30 permissions requested
Sources
2 sources
Sources
2 sources
More from this category
 AppOpsNext
 Privacy Flip
 App Lock
 AvarionX
 Amarok
 Privacify
 Anubis
 Redirect Guard
 Shelter
 手機守門哨